Rule Release for today - June 8th, 2010
Here we are again, Microsoft Tuesday for June 2010. A number of issues this month and rules to provide coverage for attack detection. Main advisory numbers for IDS/IPS coverage are MS10-033, MS10-034, MS10-035, MS10-038, MS10-039 and MS10-041. Check out the advisory and changelog
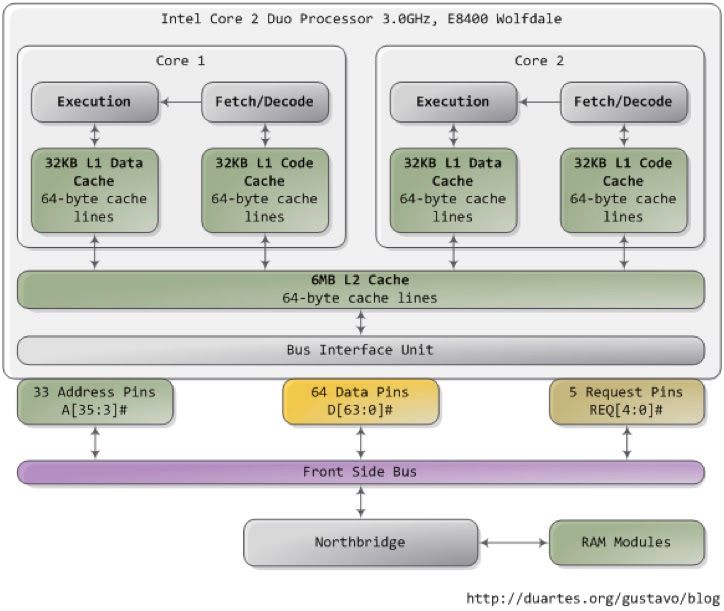
Single Threaded Data Processing Pipelines and the Intel Architecture
Or, No Performance for you, go home now. Today's blog post is a guest appearance by our Benevolent Dictator and Glorious Leader, Marty Roesch. We asked Marty for his thoughts on threading, performance and processing network data. Here's what we got: Executive Summary
Rule release for today, Tuesday May 25th, 2010
A maintenance release, new rules in web-client, web-misc, backdoor, oracle, policy and specific-threats rule sets and an extensive set of rule updates. Check it out: http://www.snort.org/vrt/advisories/2010/05/25/vrt-rules-2010-05-25.html/
Rule release for today, Tuesday May 18th, 2010
Changes to web-client, web-misc, backdoor, smtp and specific-threats rule sets. Check here: http://www.snort.org/vrt/advisories/2010/05/18/vrt-rules-2010-05-18.html for change logs etc..
Vulnerability Report - May 2010
Rule release for today, Tuesday May 11th, 2010
Microsoft Tuesday folks, just two advisories today and two rules to cover them. Read all about it here: http://www.snort.org/vrt/advisories/2010/05/11/vrt-rules-2010-05-11.html Enjoy.
Known Unknowns: The "Don't Do That" Rules
I recently had a chance to speak with several Sourcefire customers on a trip to the Tennessee/Kentucky area. While it's always nice to talk to customers and get a better idea of how people use Snort in the wild, this trip was particularly interesting, since the customers I sp
Rule release for today, Thursday April 29th, 2010
Performance update release for 2.8.6 to utilize HTTP buffers and fast_pattern. Check here for details.
Using Snort fast patterns wisely for fast rules
Anyone that's ever written their own Snort rule has wondered, at some point or another, about how to make their rule(s) faster. While some things are obvious - don't use a PCRE with a bunch of ".*" clauses, for example - others are less so. Today I'd like to