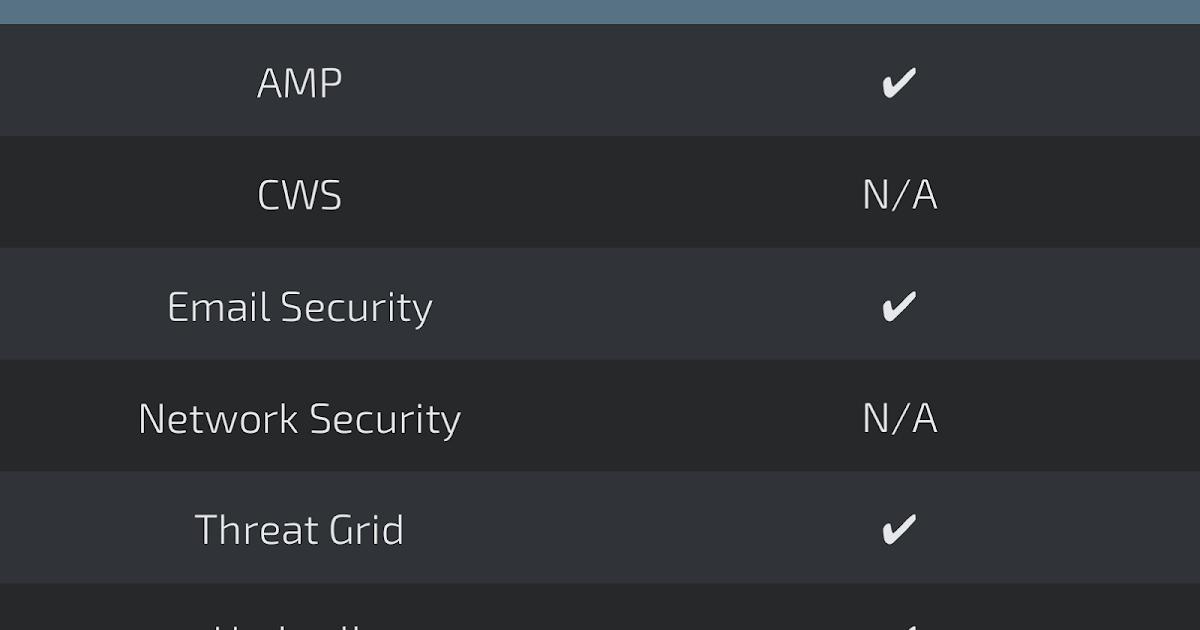
Threat Round-up for Mar 31 - Apr 7
Today, Talos is publishing a glimpse into the most prevalent threats we've observed between March 31 and April 7. As with previous round-ups, this post isn't meant to be an in-depth analysis. Instead, this post will summarize the threats we've observed by highlighting
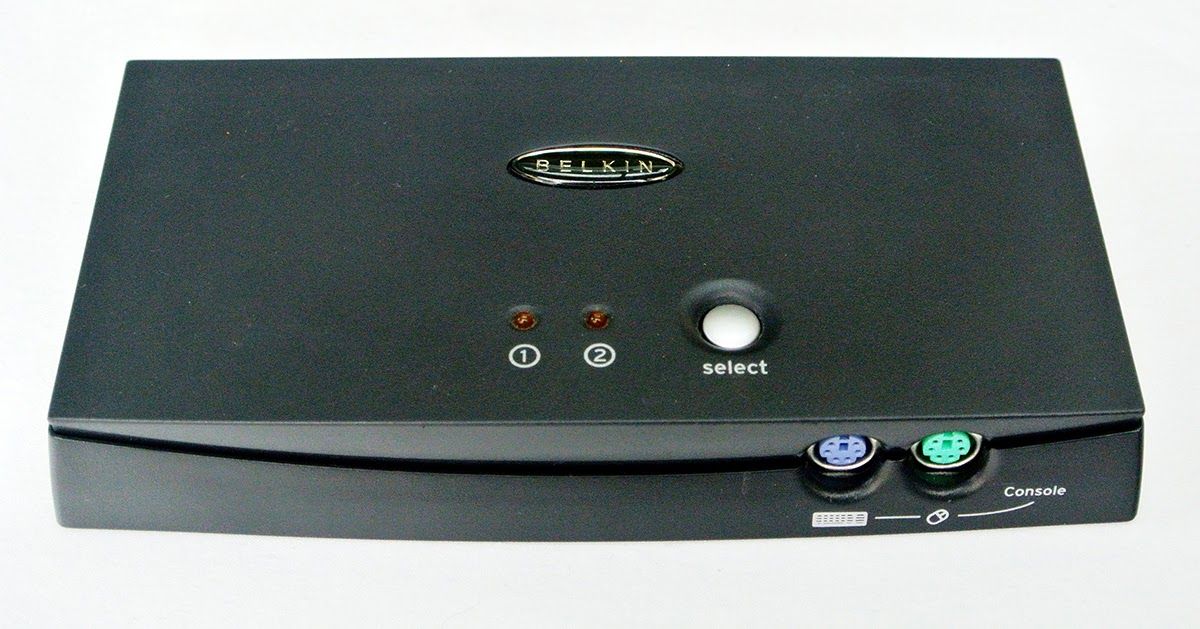
Hacking the Belkin E Series OmniView 2-Port KVM Switch
Author: Ian Payton, Security Advisory EMEAR This post is available to download as a whitepaper. Introduction Too frequently security professionals only consider software vulnerabilities when considering the risks of connecting devices to their networks and systems. When it com
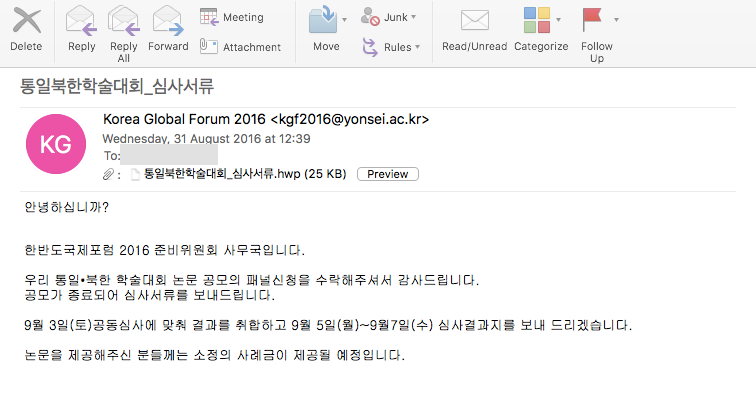
Introducing ROKRAT
This blog was authored by Warren Mercer and Paul Rascagneres with contributions from Matthew Molyett. Executive Summary A few weeks ago, Talos published research on a Korean MalDoc. As we previously discussed this actor is quick to cover their tracks and very quickly cleaned up
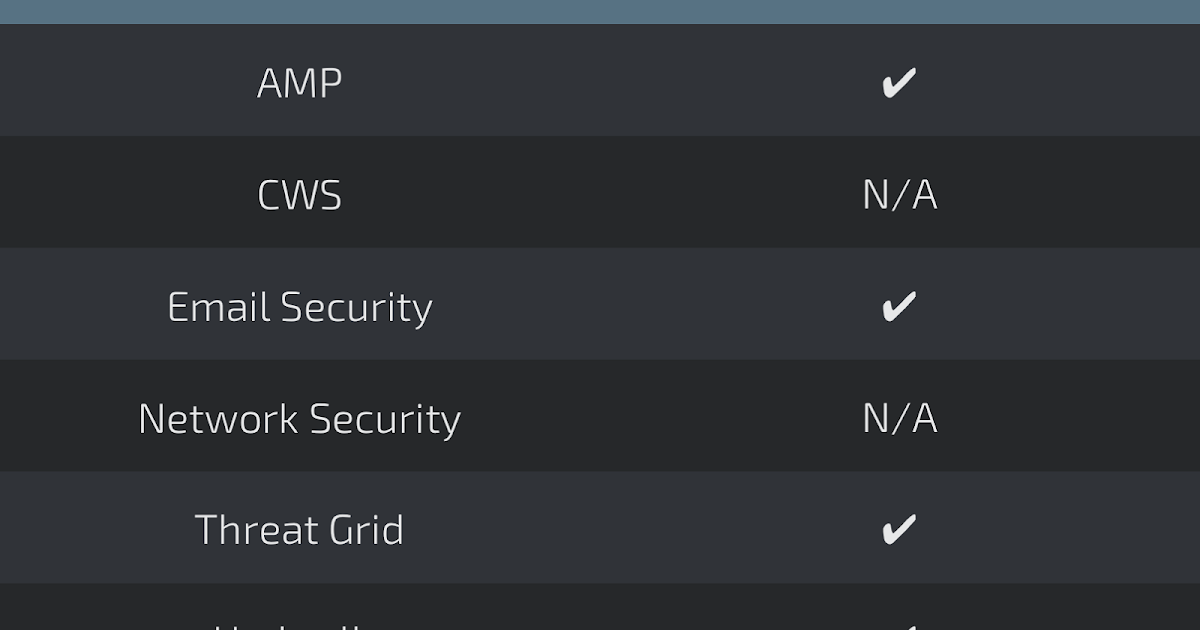
Threat Round-up for Mar 24 - Mar 31
Today, Talos is publishing a glimpse into the most prevalent threats we've observed between March 24 and March 31. As with previous round-ups, this post isn't meant to be an in-depth analysis. Instead, this post will summarize the threats we've observed by highlightin
Threat Spotlight: Sundown Matures
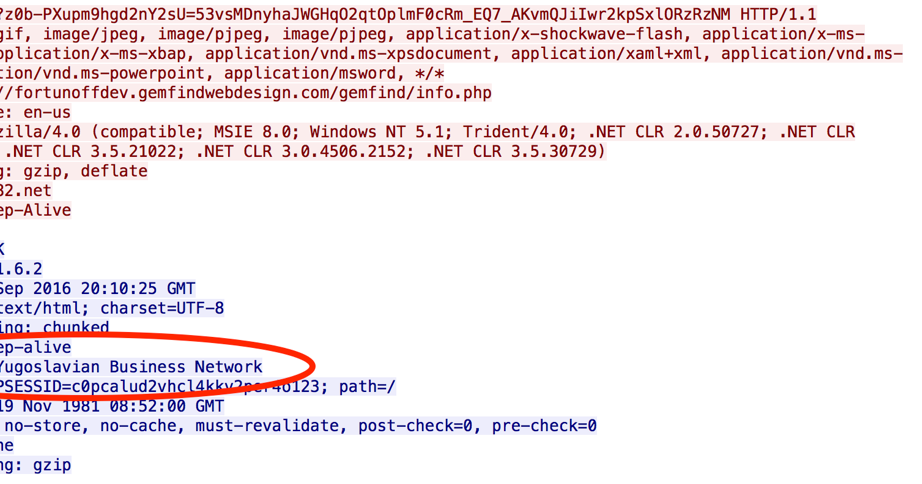
This post authored by Nick Biasini with contributions from Edmund Brumaghin and Alex Chiu The last time Talos discussed Sundown it was an exploit kit in transition. Several of the large exploit kits had left the landscape and a couple of strong contenders remain. Sundown was one
Vulnerability Spotlight: Exploiting Network Time Protocol Origin Timestamp Check Denial of Service Vulnerability
Vulnerabilities discovered by Matthew Van Gundy from Cisco ASIG Overview As a member of the Linux FoundationCore Infrastructure Initiative, Cisco is contributing to the CII effort by evaluating the Network Time Protocol daemon (ntpd) for security defects. We previously identif
Vulnerability Spotlight: Certificate Validation Flaw in Apple macOS and iOS Identified and Patched
Most people don't give much thought to what happens when you connect to your bank's website or log in to your email account. For most people, securely connecting to a website seems as simple as checking to make sure the little padlock in the address bar is present. Howeve
Threat Round-up for the Week of Mar 20 - Mar 24
Today, Talos is publishing a glimpse into the most prevalent threats we've observed over the past week. As with previous round-ups, this post isn't meant to be an in-depth analysis. Instead, this post will summarize the threats we've observed by highlighting key behav
How Malformed RTF Defeats Security Engines
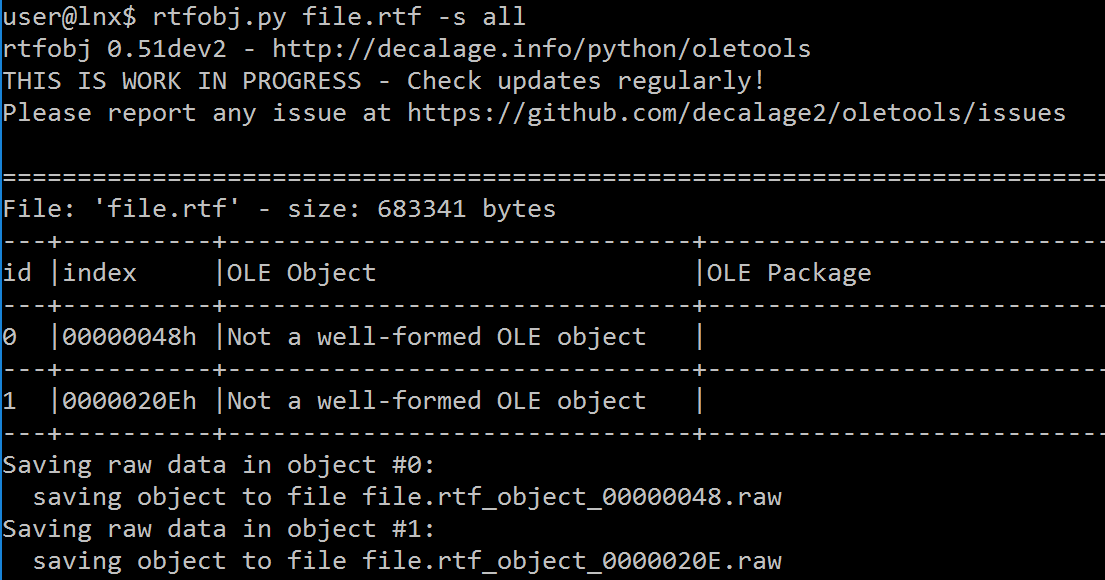
This post is authored by Paul Rascagneres with contributions from Alex McDonnell Executive Summary Talos has discovered a new spam campaign used to infect targets with the well known Loki Bot stealer. The infection vector is an RTF document abusing an old exploit (CVE-2016-7193