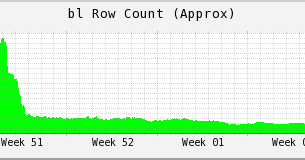
Without Necurs, Locky Struggles
This post authored by Nick Biasini with contributions from Jaeson Schultz Locky has been a devastating force for the last year in the spam and ransomware landscape. The Locky variant of ransomware has been responsible for huge amounts of spam messages being sent on a daily basis
Vulnerability Spotlight: Multiple Code Execution Vulnerabilities in Oracle Outside In Technology
These vulnerabilities were discovered by Aleksandar Nikolic of Cisco Talos. Summary Oracle's Outside In Technology (OIT) is a set of SDKs that software developers can use to perform various actions against a large number of different file formats. According to the OIT web
Vulnerability Spotlight: Exploiting the Aerospike Database Server
Vulnerabilities discovered by Talos Talos is disclosing multiple vulnerabilities discovered in the Aerospike Database Server. These vulnerabilities range from memory disclosure to potential remote code execution. This software is used by various companies that require a high per

Shadow Brokers Malware Coverage
The Shadow Brokers released what appears to be a series of windows rootkit components in a farewell message. The malware released included many Windows malware files that supposedly all trigger as either “equationdrug.generic” or “equationdrug.k” by the Kaspersky security produc
Microsoft Patch Tuesday - January 2017
Happy New Year to our readers! Today marks the first Patch Tuesday of 2017 with Microsoft releasing their monthly set of bulletins designed to address security vulnerabilities. This month's release is relatively light with 4 bulletins addressing 3 vulnerabilities. Two bulleti
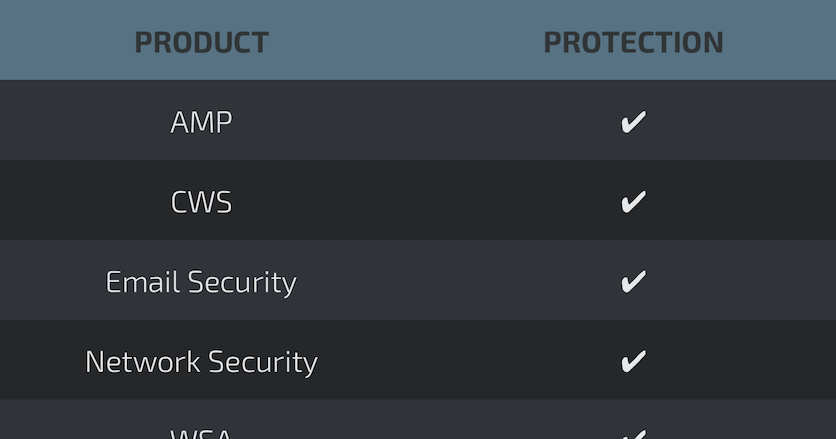
Cisco Coverage for 'GRIZZLY STEPPE'
Over the past several weeks, there have been ongoing discussions regarding cyber attacks that have occurred against several political, governmental, and private sector entities in the United States. These discussions have revolved around allegations that these cyber attacks were
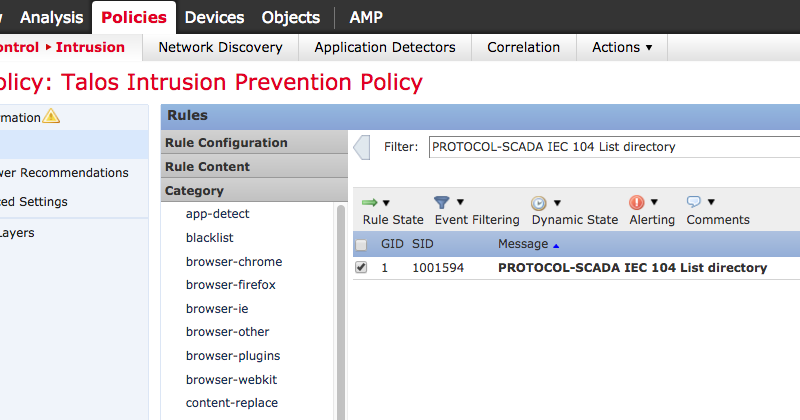
IEC 104 Protocol Detection Rules
IEC 60870-5-104 Protocol Detection Rules Cisco Talos has released 33 Snort rules which are used to analyze/inspect IEC 60870-5-104 network traffic. These rules will help Industrial Control Systems/Supervisory Control and Data Acquisition (ICS/SCADA) asset owners to allow the iden
Vulnerabiity Spotlight: Tarantool Denial of Service Vulnerabilities
Vulnerabilities discovered by Talos Talos is disclosing two denial of service vulnerabilities (CVE-2016-9036 & CVE-2016-9037) in Tarantool. Tarantool is an open-source lua-based application server. While primarily functioning as an application server, it is also capable of p
In the Eye of the Hailstorm
This blog post was authored by Jakob Dohrmann, David Rodriguez, and Jaeson Schultz. The Cisco Talos and Umbrella research teams are deploying a distributed hailstorm detection system which brings together machine learning, stream processing of DNS requests and the curated Talos