Microsoft Patch Tuesday - May 2016
This post is authored by Holger Unterbrink. Patch Tuesday for May 2016 has arrived where Microsoft releases their monthly set of security bulletins designed to address security vulnerabilities within their products. This month's release contains 16 bulletins addressing 33 vu
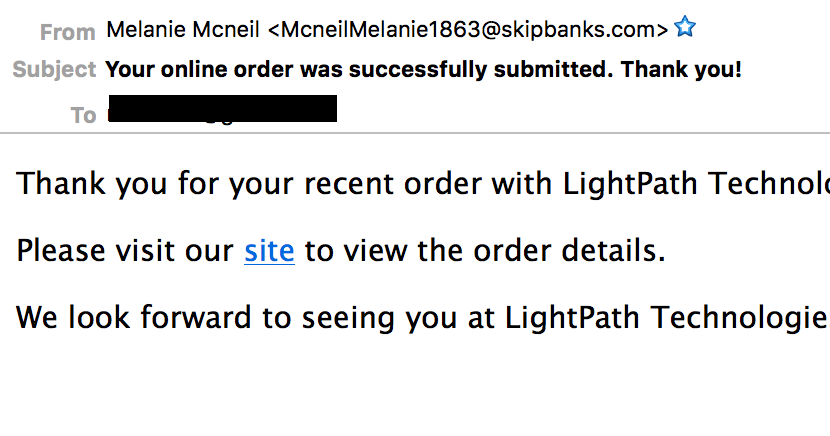
Angler Catches Victims Using Spam as Bait
This post is authored by Nick Biasini with contributions from Erick Galinkin and Alex McDonnell Exploit kits have been a recurring threat that we've discussed here on this blog as a method of driving users to maliciousness. Users typically encounter exploit kit landing pages
Threat Spotlight: Spin to Win...Malware
This post was authored by Nick Biasini with contributions from Tom Schoellhammer and Emmanuel Tacheau. The threat landscape is ever changing and adversaries are always working to find more efficient ways to compromise users. One of the many ways that users are driven to maliciou
Cryptolocker 4 White Paper Available: The Evolution Continues
We are pleased to announce the availability of the Cryptolocker 4 white paper. Over the past year, Talos has devoted a significant amount of time to better understanding how ransomware operates, its relation to other malware, and its economic impact. This research has proven valu
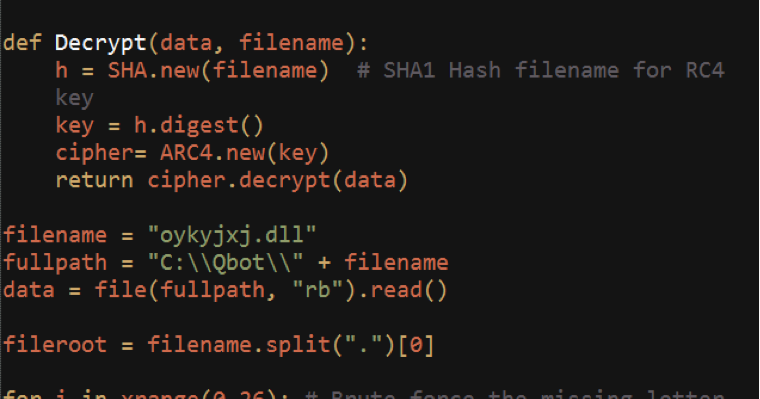
Research Spotlight: The Resurgence of Qbot
The post was authored by Ben Baker. Qbot, AKA Qakbot, has been around for since at least 2008, but it recently experienced a large surge in development and deployments. Qbot primarily targets sensitive information like banking credentials. Here we are unveiling recent changes to
The "Wizzards" of Adware
This post was authored by Warren Mercer with contributions from Matthew Molyett Executive Summary Talos posted a blog, September 2015, which aimed to identify how often seemingly benign software can be rightly condemned for being a piece of malware. With this in mind, this blog

Vulnerability Spotlight: Further NTPD Vulnerabilities
As a member of the Linux Foundation Core Infrastructure Initiative, Cisco is contributing to the CII effort by evaluating the Network Time Protocol daemon (ntpd) for security defects. We previously identified a series of vulnerabilities in the Network Time Protocol daemon; throug
Threat Spotlight: Exploit Kit Goes International Hits 150+ Countries
Overview Talos is constantly monitoring the threat landscape and exploit kits are a constantly evolving component of it. An ongoing goal of Talos is to expose and disrupt these kits to protect the average internet user being targeted and compromised. We were able to gain unprece
Oracle OIT Image Export SDK libvs_pdf XRef Index Code Execution Vulnerability
This post was authored by Aleksandar Nikolic and Jaeson Schultz. Talos has recently discovered a vulnerability in Oracle’s Outside In Technology Image Export SDK which, when exploited, allows an attacker to overflow the heap, leading to arbitrary code execution. The vulnerabil