Threat Spotlight: "Kyle and Stan" Malvertising Network Threatens Windows and Mac Users With Mutating Malware
This post was authored by Shaun Hurley, David McDaniel and Armin Pelkmann. Malware was discovered by Richard Harman. Update 2014-09-22: Updates on this threat can be found here Have you visited amazon.com, ads.yahoo.com, www.winrar.com, youtube.com, or any of the 74 domains lis

Danger at the Retail Point of Sale
This blog post was authored by Martin Lee and Jaeson Schultz. With the announcement that yet another major retailer has allegedly been breached, it is important to review how attackers compromise retail systems and how such intrusions can be prevented. In this latest case, retai
Malware Using the Registry to Store a Zeus Configuration File
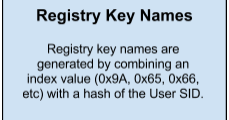
This blog was co-authored by Andrea Allievi. A few weeks ago I came across a sample that was reading from and writing a significant amount of data to the registry. Initially, it was thought that the file may be a binary, but after some analysis it was determined that the file is

Discovering Dynamically Loaded API in Visual Basic Binaries
Performing analysis on a Visual Basic (VB) script, or when Visual Basic is paired with the .NET Framework, becomes an exercise of source code analysis. Unfortunately when Visual Basic is compiled to a Windows Portable Executable (PE) file it can become a nightmare for many malwar

Snowshoe Spam Attack Comes and Goes in a Flurry
This post is authored by Alex Chiu, Jaeson Schultz and Craig Williams. Every so often, we observe certain spam campaigns that catch our interest. On August 15, we observed a particular spam campaign that caught our attention because it was using "snowshoe" spam techniq

The Windows 8.1 Kernel Patch Protection
In the last 3 months we have seen a lot of machines compromised by Uroburos (a kernel-mode rootkit that spreads in the wild and specifically targets Windows 7 64-bit). Curiosity lead me to start analyzing the code for Kernel Patch Protection on Windows 8.1. We will take a glance
Microsoft Update Tuesday August 2014: Media Center and Internet Explorer
This month’s Microsoft Update Tuesday is relatively light compared to the major update of last month. We’re getting a total of six bulletins this month, two marked critical, three as important and finally one moderate. These six bulletins cover a total of 29 CVEs, most of which a
Apple ID Harvesting, now this is a good phish.
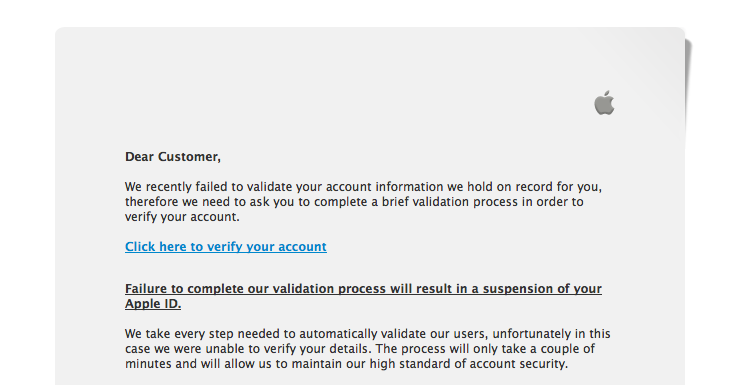
Phishing isn't new. "So, why are you writing about it?", you ask. I received this one today and it was very well done, so I thought I'd write it up. Chances are, you've seen these before: If you are familiar with Apple Verification emails, you'll not
Microsoft Update Tuesday July 2014: light month, mostly Internet Explorer
This month’s Microsoft Update Tuesday is relatively light compared to the major update of last month. We’re getting a total of six bulletins this month, two marked critical, three as important and finally one moderate. These six bulletins cover a total of 29 CVEs, most of which a