Continued analysis of the LightsOut Exploit Kit
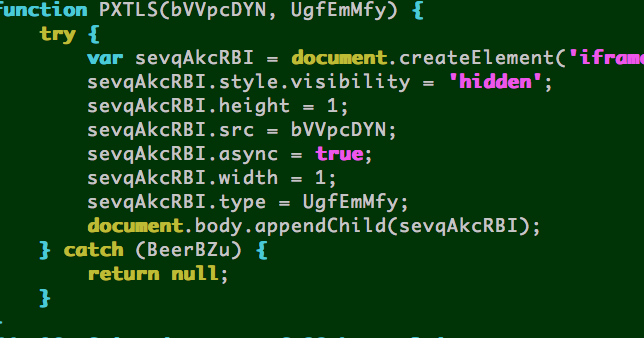
At the end of March, we disclosed the coverage of an Exploit Kit we called “Hello”: http://blog.talosintel.com/2014/03/hello-new-exploit-kit.html, or “LightsOut”, we thought we’d do a follow up post to tear this exploit kit apart a bit more. This variant of the LightsOut exploit
Anatomy of an exploit: CVE 2014-1776
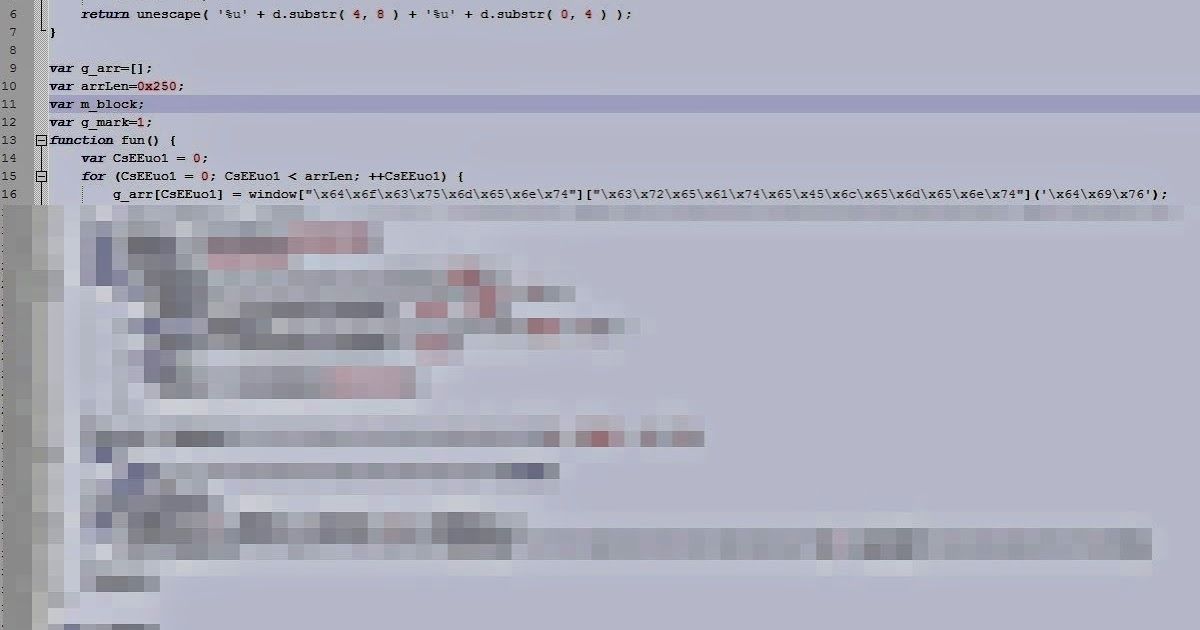
This post is co-authored by Alex McDonnell, Brandon Stultz, Joel Esler, Patrick Mullen, Armin Pelkmann, and Craig Williams When the Internet Explorer 0-day CVE 2014-1776 was announced, we turned to our intelligence feeds for more information. In the course of taking it apart we
Internet Explorer & Adobe Flash 0-Day Coverage
Recently several "0day" releases have come out in the security world, and the VRT has released coverage for two critical vulnerabilities, so we wanted to notify you of this coverage so you can use the SIDs to protect your environment. Microsoft Internet Explorer 0day C

Snake Campaign: A few words about the Uroburos Rootkit
Over the past few days, analyzing the new Uroburos (aka Turla) rootkit has been exciting. That's because the sample dropper (MD5: a86ac0ad1f8928e8d4e1b728448f54f9) includes a lot of clever features. We don’t want to rehash research already publicly available, but we will expa
Heartbleed for OpenVPN
Core to the VRT's mission is challenging the general intrusion detection industry's view of "adequate" vulnerability coverage. One way we do this is to seek out new attack vectors for critical vulnerabilities the industry may have overlooked and take the initiat
Performing the Heartbleed Attack After the TLS Handshake
Over the past several days, many IPS rules for detecting the Heartbleed attack have been suggested that attempt to compare the TLS message size to the heartbeat message size. This method works with most of the Proof-of-Concept attacks out there, which perform the Heartbleed atta
Heartbleed Continued - OpenSSL Client Memory Exposed
The Heartbleed vulnerability is bad. Not only does it pose a risk to servers running the vulnerable version of OpenSSL (1.0.1 through 1.0.1f) with heartbeats enabled, it also poses a serious risk to clients running the vulnerable versions. OpenSSL clients process heartbeats usin
Heartbleed Memory Disclosure - Upgrade OpenSSL Now!
Heartbleed is a serious vulnerability in OpenSSL 1.0.1 through 1.0.1f. If you have not upgraded to OpenSSL 1.0.1g or installed a version of OpenSSL with -DOPENSSL_NO_HEARTBEATS it is strongly recommended that you do so immediately. This vulnerability allows the attacker to rea
Microsoft Update Tuesday: April 2014, two final XP and Office 2003 fixes
It’s the last Microsoft Update Tuesday before the end-of-life of both Windows XP and Office 2003 and Microsoft is patching two vulnerabilities that also impact XP and two that also impact Office 2003 this month. All-in-all it’s a relatively light month this time around with only